Configuration

Athena Server is configured through appsettings.json. Values you save in the console go to appsettings.local.json in the data directory, and environment variables override both (sections use a double-underscore separator, e.g. Server__PublicUrl).

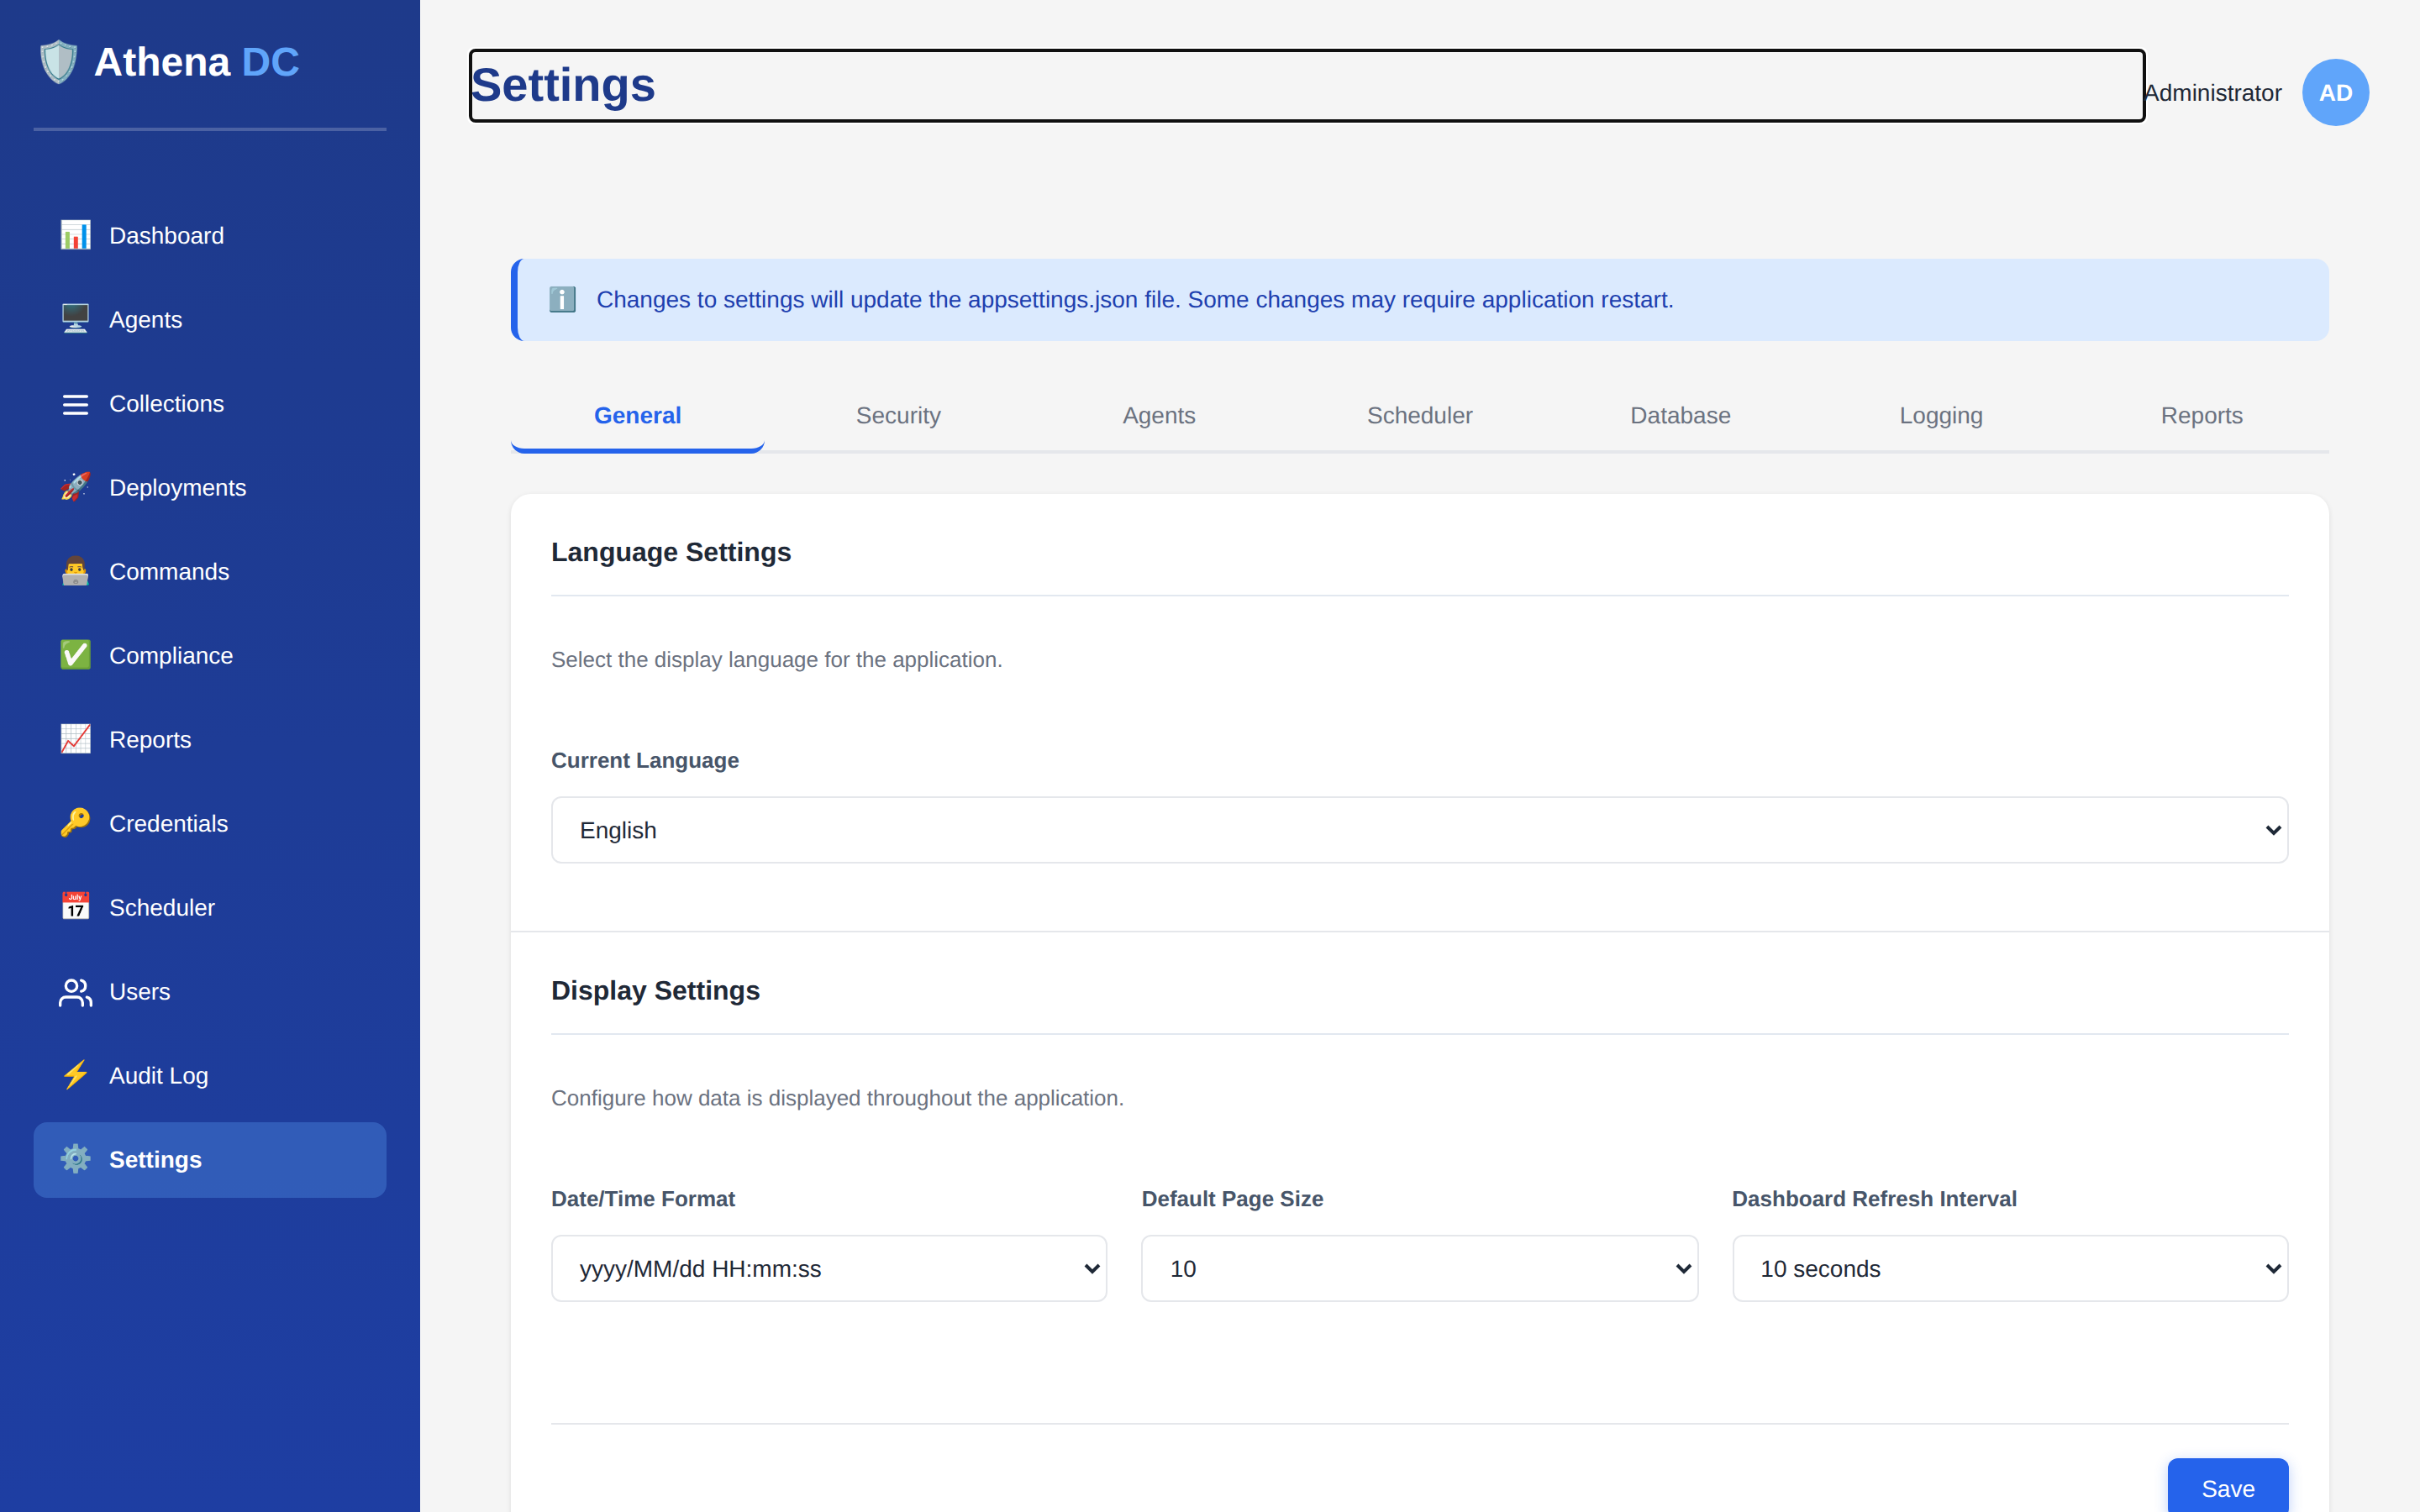
The Settings screen in Athena
Settings → General — language and display options; each tab maps to a group of settings, saved to appsettings.local.json.

Configuration sources#

Settings are layered, with later sources overriding earlier ones. The precedence, lowest to highest, is:

  1. appsettings.json: the shipped defaults, baked into the image. The server never writes to this file.
  2. appsettings.<Environment>.json: an optional environment overlay, such as appsettings.Production.json (the container runs as Production).
  3. appsettings.local.json in the server's data directory: every value you save on a Settings tab is written here (/app/data/appsettings.local.json in the container, or next to the server executable on a direct install). The file appears on the first save. Changes are picked up without a restart, although the Settings page notes that some settings still need one.
  4. secrets.json in the data directory: per-install secrets the server generates on first start.
  5. Environment variables: ideal for secrets and host-specific values, passed to the container with -e.
  6. Command-line arguments passed when the server process starts (highest precedence).

Because appsettings.local.json sits above the shipped and environment files, a value saved in the console beats them. An environment variable or command-line argument still beats a saved value. When that happens, the save shows a warning; see Configuration Override Warnings.

A nested JSON key maps to an environment variable by joining the section and key names with a double underscore. For example, the Server:PublicUrl setting is overridden by:

Server__PublicUrl=https://athena.example.com:8443
Keep secrets out of config files

Provide Jwt__Secret and RemoteSession__Turn__StaticAuthSecret as environment variables rather than writing them into appsettings.json. The JWT secret signs the console's login tokens and the TURN secret authorizes remote-session relay credentials — treat both like passwords.

Database#

The Database section selects the storage provider and connection.

KeyDefaultNotes
ProviderSqliteDefault. Also supports PostgreSQL.
ConnectionStringData Source=athena.dbProvider-specific connection string.
HeartbeatBatchDelayMs3000Batching window for agent heartbeat writes, in milliseconds.

SQL Server is not shipped — only the SQLite and PostgreSQL provider plugins exist. For a step-by-step guide to running on PostgreSQL — the connection string format, schema creation, and how to verify it — see Using PostgreSQL for the Database.

Server & ports#

The Server section controls the listening ports, TLS and the externally reachable URL. To replace the auto-generated certificate with your own and run behind a reverse proxy, see Server TLS Certificate.

KeyDefaultNotes
WebPort8443Web console / API port.
ApiPort8444Agent gateway port (gRPC over HTTP/2).
TlsEnabledtrueTerminate TLS on Kestrel.
Hostnames—Hostnames the server answers on.
WebCertPath—Path to the server TLS certificate (PFX).
WebCertPassword—Password for the PFX certificate.
PublicUrl—Externally reachable base URL, e.g. https://athena.example.com:8443.

gRPC#

The nested Grpc section tunes the agent gateway message limits.

KeyDefaultNotes
MaxReceiveMessageSize6710886464 MB — sized for video and file transfers.
MaxSendMessageSize6710886464 MB — sized for video and file transfers.
EnableDetailedErrorstrueInclude detailed error information on gRPC faults.

PKI#

The Pki section governs the built-in certificate authority that issues and renews agent certificates.

KeyDefaultNotes
CertificatesPath./pkiWhere the CA and issued certificates are stored.
CaSubjectCN=Athena Root CA, O=Athena Deploy CenterDistinguished name of the root CA.
CaValidityYears10Root CA lifetime, in years.
AgentCertValidityDays60Issued agent certificate lifetime, in days.
AutoRenewBeforeDays7Renew agent certificates this many days before expiry.
KeySize2048Agent certificate key size, in bits.
RootCaKeySize4096Root CA key size, in bits.
EnableAutoRenewaltrueRun the automatic renewal job.
AutoRenewalCheckIntervalHours6How often the renewal job runs, in hours.

Authentication (JWT)#

The Jwt section configures the tokens issued to the web console.

KeyDefaultNotes
Secret—Signing secret. Environment variable only (Jwt__Secret).
IssuerAthenaToken issuer claim.
AudienceAthenaToken audience claim.
ExpirationMinutes15Access token lifetime, in minutes.

Security#

The Security section controls session, lockout, rate-limiting and password rules.

KeyDefaultNotes
SessionTimeoutMinutes3Idle session timeout, in minutes.
MaxFailedLoginAttempts5Failed sign-ins before lockout.
LockoutDurationMinutes15How long an account stays locked, in minutes.
HardLockThreshold30Failed attempts before a hard lock.
MaxRequestsPerMinutePerIp10Per-IP request ceiling, per minute.
EnableJwtSecretRotationtrueRotate the JWT signing secret automatically.
AgentTokenValidityDays90Agent token lifetime, in days.

PasswordPolicy#

KeyDefault
MinimumLength8
RequireUppercasetrue
RequireLowercasetrue
RequireDigittrue
RequireSpecialCharacterfalse

An Admin can review and change the session, lockout, and password-policy values from the console or API without editing this file — see Security Settings.
ConnectionRateLimit#

KeyDefaultNotes
PermitLimit20Connections permitted per window.
WindowSeconds60Rate-limit window, in seconds.

Audit#

The Audit section controls the audit trail sink and optional syslog forwarding.

KeyDefaultNotes
ProviderFileAudit sink.
DirectoryAuditLogsDirectory for audit log files.
FilePrefixauditFilename prefix for audit logs.
BufferSize—Write buffer size.

Syslog#

KeyDefaultNotes
EnabledfalseForward audit events to syslog.
Host—Syslog collector host.
Port514Syslog port.
TransportUdpTransport protocol: Udp, Tcp, or TcpTls (TLS 1.2/1.3, RFC 5425; usually port 6514).
FormatRfc5424Syslog message format.
Facility16Syslog facility code.
BufferSize10Syslog send buffer size.
TlsCaCertificatePem—TcpTls only. PEM of the CA that issued the collector's certificate; when set, only this CA is trusted. Empty = the OS trust store.
TlsSkipCertificateValidationfalseTcpTls only. Lab use only — skips checking the collector's certificate.

For forwarding to a SIEM, see Audit & SIEM and Encrypting forwarding with TLS.

Packages & recording#

Packages#

KeyDefaultNotes
StoragePath./packagesWhere uploaded deployment packages are stored.
MaxUploadSizeGB15Maximum package upload size, in gigabytes.
BaseUrl—Externally reachable URL agents use to fetch packages.
TokenSecret—Secret used to sign package download tokens.

Recording#

KeyDefaultNotes
Enabled—Record remote sessions.
StoragePath./recordingsWhere session recordings are stored.
RetentionDays30How long recordings are kept, in days.
MaxSessionSizeMB2048Maximum recording size per session, in megabytes.

Remote session#

The RemoteSession section controls remote desktop and command sessions.

KeyDefaultNotes
EnableHelperLaunchtrueAllow launching the remote helper.
MaxSessionDurationMinutes120Maximum session length, in minutes.
ReconnectWindowSeconds30Window to reconnect a dropped session, in seconds.
WebRtcEnabledtrueUse WebRTC for the media channel.

Turn (coturn)#

KeyDefaultNotes
SchemeturnTURN URI scheme.
Host—coturn host.
Port3478coturn port.
TransportudpTURN transport.
CredentialTtlSeconds600Lifetime of generated TURN credentials, in seconds.
StaticAuthSecret—Environment variable only (RemoteSession__Turn__StaticAuthSecret).

For the operator-facing workflow, see Remote Commands & Desktop.

Other settings#

Localization#

KeyDefault
Languageen
SupportedLanguages["en"]

DefaultAdmin#

KeyDefaultNotes
UsernameadminSeeded administrator username.
Password—Initial password — change on first sign-in.
DisplayName—Administrator display name.
Email—Administrator email address.

Scheduler#

KeyDefault
CronBuilderModeVisual
DefaultDeploymentTimeoutMinutes120

Swagger#

KeyDefault
Enabledtrue
RoutePrefixapi-docs
TitleAthena Deploy Center API

General#

KeyDefault
ApplicationNameAthena Deploy Center
DefaultPageSize10
DashboardRefreshInterval10

Logging#

KeyDefault
DirectoryLogs
RetentionDays30

Minimal example#

A minimal appsettings.json with the most common sections. Keep real secret values out of this file — supply them via environment variables.

{
  "Database": {
    "Provider": "Sqlite",
    "ConnectionString": "Data Source=athena.db"
  },
  "Server": {
    "WebPort": 8443,
    "ApiPort": 8444,
    "TlsEnabled": true,
    "WebCertPath": "/app/certs/server.pfx",
    "PublicUrl": "https://athena.example.com:8443"
  },
  "Jwt": {
    "Secret": "<set via Jwt__Secret env var>",
    "Issuer": "Athena",
    "Audience": "Athena",
    "ExpirationMinutes": 15
  },
  "DefaultAdmin": {
    "Username": "admin",
    "Password": "<change on first sign-in>",
    "DisplayName": "Administrator",
    "Email": "admin@example.com"
  }
}